The federal government has substantial sovereign immunity. That means that it can't be sued without its permission. Private companies don't have that protection, and you should keep that distinction in mind as you read what follows.
On March 27, 2026, the White House released an official mobile app. Within hours, two independent security researchers, one posting under the handle Thereallo1 and one from Atomic Computer Services,2 had decompiled the Android APK and the iOS binary and published their findings. They worked independently and reached many of the same conclusions, suggesting the same decisions went into both packages. What they found is the kind of thing that gets a private company sued.
The researchers found collection the app never disclosed
The app is a content portal that uses GPS tracking
The Android APK includes OneSignal's full location-tracking framework, with polling intervals hardcoded to 4.5 minutes in the foreground and 9.5 minutes in the background.3 The iOS binary requests location access even when the app isn't in use and includes the same location-framework symbols.4
That matters because the app is a news reader. It serves articles, live streams, photo galleries, and policy pages. It has no map, local content, geofencing, or weather. Nothing in the app would justify collecting your GPS coordinates every 4.5 minutes.
The tracking is not unconditionally active. Three conditions must be met: a software flag must be set to true, the user must grant location permission at the OS level, and the device must have a location provider.5 Whether the JavaScript layer currently sets that flag could not be determined from the compiled code alone. The research shows the entire infrastructure is present, operational, and one function call away from running.
The app told Apple it collects nothing, and the code says otherwise
Apple requires apps using third-party SDKs to file a privacy manifest (a formal disclosure of what data the app collects) that feeds the App Store's privacy nutrition labels.6 The White House app's manifest declares an empty data collection array and sets the tracking flag to false.7
The compiled app actually collects GPS coordinates, device identifiers, behavioral analytics, session data, notification engagement records, and user identity data.8 Apple's App Review Guidelines require the manifest to accurately reflect how the app collects data.9 This one does not.
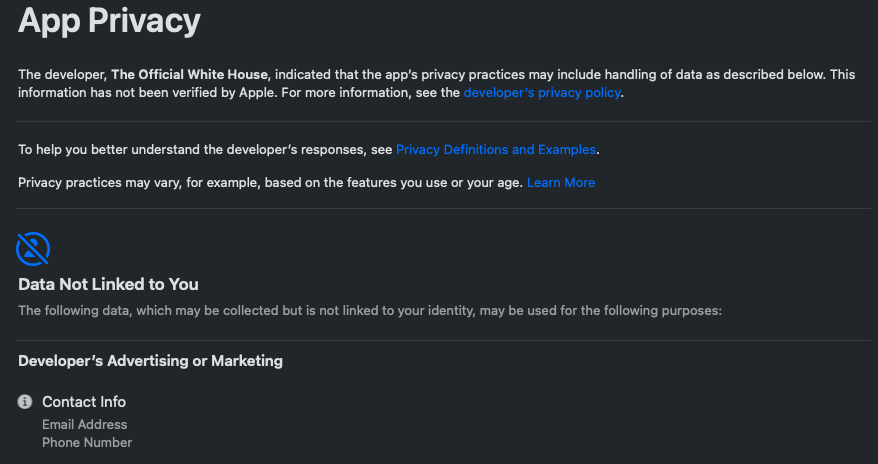
The privacy policy doesn't help. Apple links the app's listing to the White House's privacy page at https://www.whitehouse.gov/privacy/, which was plainly written for the website. It says nothing about what the app does. Meanwhile, the App Store listing assures you that, while the app collects your contact information for marketing purposes, it doesn't link that information to you.
Injected JavaScript takes away your ability to choose
Every page loaded in the app's in-app browser receives an injected JavaScript snippet before rendering. That snippet hides cookie consent banners, GDPR notices, OneTrust popups, privacy banners, login walls, signup walls, and paywall elements.10 It also sets up a continuous observer that watches for consent elements added after the page loads and suppresses them too.11
The researchers found this script in the Hermes bytecode string table and confirmed it on the native side. The code hunts for consent elements by name and keeps hunting after the page loads.
Consider what that means legally. The app systematically strips consent mechanisms from third-party websites on behalf of its users, without those websites' knowledge or agreement. U.S. law says relatively little about this directly. European law says much more, as we'll see below.
Third-party code runs inside the app without verification
Six social media widgets from Elfsight, a company that originated in Russia, load JavaScript at runtime from Elfsight's CDN. The loader runs in two stages. It pulls a server response, then dynamically injects additional scripts. Because those scripts come straight from Elfsight's servers with no integrity check, Elfsight can change the code that executes in the app at any time, without an app update or an App Store review.12
The app ships code from a company on the U.S. Entity List
The Exodus Privacy static analysis of the Android APK identifies Huawei Mobile Services (HMS) Core in the build.13 HMS Core is a product of Huawei Technologies Co., Ltd.14 Huawei is on the Commerce Department's Entity List,15 the formal U.S. government register of companies subject to export restrictions on national security and foreign policy grounds.16 The original designation, made in May 2019, carries a presumption of denial on export license applications and has been amended nine times since.17
The national security concerns behind that designation were not new in 2019. In February 2018, during the first Trump administration, the heads of six U.S. intelligence agencies, including the CIA, FBI, NSA, and the Director of National Intelligence, told the Senate Intelligence Committee that they would not recommend Americans use Huawei products or services. Then-FBI Director Christopher Wray said they were "deeply concerned about the risks of allowing any company or entity that is beholden to foreign governments that don't share our values to gain positions of power inside our telecommunications networks."18 The Entity List designation followed fifteen months later.
HMS Core is close to a technical prerequisite for distribution on Huawei's AppGallery, the platform Huawei built because the Entity List designation cut it off from the Google ecosystem.19 A search of AppGallery shows the White House app is not listed there.20 The HMS integration is in the build regardless. The code can't say whether that reflects a developer oversight, a compatibility decision, or an intent to distribute through Huawei's platform at some point. The code does establish that the Executive Office of the President released an official application containing an SDK from a company the U.S. government has formally designated a national security concern.
A private company shipping this app would face real exposure
A private company that shipped an application like this would face meaningful regulatory and litigation risk on several fronts.
The disclosure mismatch is the core problem
A privacy policy written for a website cannot serve as the disclosure for a mobile application that collects GPS coordinates, device identifiers, and behavioral analytics. The FTC has brought Section 5 enforcement actions against companies whose privacy representations materially misrepresented their actual data collection practices.21 A privacy manifest that says there is nothing to see here, attached to an app that ships several analytics packages and quietly overrides users' privacy choices on other sites, is not a gray area.
None of this is new. I covered the mechanics of privacy policy gaps in an earlier post on the distance between privacy statements and reality.22 The White House app is a vivid example of that problem in the wild.
Location data carries heightened obligations
Several states treat precise geolocation as sensitive personal information subject to additional requirements. Under the CCPA, as amended by the CPRA, precise geolocation is sensitive personal information and is subject to a right to limit its use.23 Washington's My Health My Data Act covers geolocation data that could infer health information, including visits to certain locations.24 The Texas Data Privacy and Security Act classifies precise geolocation as "sensitive data."25 Continuous background GPS collection with no disclosed purpose tied to any app feature draws regulatory attention.
Suppressing consent banners is its own theory of liability
From a U.S. perspective, cookie consent banners are largely a website operator's governance mechanism rather than a legal right held by app users. The EU treats them differently. Under the ePrivacy Directive, the banner is how a website obtains the consent the law requires before it stores or reads information on a user's device.26 An application that programmatically removes that mechanism across every external site, without the user's express consent or the website operator's knowledge, is doing something European regulators would find interesting. For a private company with European operations or European users, this is not a theoretical problem.
Your SDKs' collection is your collection
When a third-party SDK collects data inside your application, most privacy laws treat that collection as yours. You are responsible for disclosing it, governing it, and ensuring your agreements with the SDK vendor meet applicable data-processing requirements.27 An app that loads live, modifiable JavaScript from a foreign CDN with no integrity verification has data practices partly defined by whoever controls that CDN at any given moment. For a private company, "we didn't write that code" is not a defense.
Anyone can read your app the way they read this one
Neither researcher needed special access to find any of this.
They downloaded a free app from the App Store and Google Play. What followed was decompilation and static analysis with freely available tools: JADX to reconstruct source from Android bytecode, and standard macOS utilities to inspect the iOS binary. There was no privileged access, no traffic interception, and no authentication bypass. Anyone with the right tools and a bit of know-how can read the Hermes bytecode, the AndroidManifest, the Expo config, and the compiled SDK list.
Your app is equally readable.
If you have not recently done a privacy-focused review of your mobile applications, the questions are straightforward. What SDKs are compiled into your builds, and do your disclosures account for all of them? Do the permissions in your manifests and App Store privacy manifests match what the app actually requests at runtime? Was your privacy policy written for a website and never updated when you shipped an app?
The White House app was built by a company incorporated nine days before launch.28 That timeline shows in the code, and almost any half-decent QA process would have caught these problems quickly. But mismatched disclosures, undisclosed third-party data flows, and collection without a purpose are not unique to rushed government contractors. They show up across the commercial app ecosystem, sometimes at companies with real compliance programs and real lawyers, because developers were so preoccupied with whether they could that they didn't stop to think about whether they should.29
The sovereign immunity that shields the federal government from the consequences of poor choices doesn't apply to your company. Review your app's data collection and the disclosures that should govern it before someone else does it for you.
This post does not constitute legal advice. Readers should consult competent legal counsel before taking action based on the analysis presented here.
Footnotes
- Thereallo, I Decompiled the White House's New App, Thereallo (Mar. 28, 2026), http://thereallo.dev/blog/decompiling-the-white-house-app. ↩︎
- Atomic Computer Services, Security Analysis of the Official White House iOS App, atomic.computer (Mar. 27, 2026), https://www.atomic.computer/blog/white-house-app-security-analysis/. ↩︎
- Thereallo, supra note 1 (citing
LocationConstants.java:FOREGROUND_UPDATE_TIME_MS = 270000,BACKGROUND_UPDATE_TIME_MS = 570000). ↩︎ - Atomic Computer Services, supra note 2 (citing
NSLocationAlwaysAndWhenInUseUsageDescriptioninInfo.plistand symbol analysis ofOneSignalLocation.framework). ↩︎ - Thereallo, supra note 1 (identifying three activation gates: (1) the
_isSharedflag, (2) Android runtime location permission, and (3) presence of a location provider). ↩︎ - Apple Inc., Third-Party SDK Requirements, Apple Developer Support, https://developer.apple.com/support/third-party-SDK-requirements/ (last visited Mar. 30, 2026). ↩︎
- Atomic Computer Services, supra note 2 (Finding 3). ↩︎
- Id. (comparing
NSPrivacyCollectedDataTypes: []inPrivacyInfo.xcprivacyagainst binary and framework analysis showing GPS coordinates, device identifiers, behavioral analytics, session data, notification engagement, and user identity data). ↩︎ - Apple Inc., App Review Guidelines, Apple Developer, https://developer.apple.com/app-store/review/guidelines/#data-collection-and-storage (last visited Mar. 30, 2026). ↩︎
- Thereallo, supra note 1 (Consent/Paywall Bypass Injector); Atomic Computer Services, supra note 2 (Finding 5). ↩︎
- Thereallo, supra note 1 (reproducing injected JavaScript from Hermes bytecode string table and confirming via
RNCWebViewManagerImpl.javaandRNCWebView.java). ↩︎ - Atomic Computer Services, supra note 2 (citing Tracxn company profile for Elfsight as starting in Tula, Russia, and subsequently redomiciling to Andorra, and analyzing
platform.jstwo-stage loader and absence of Subresource Integrity hashes). ↩︎ - εxodus, Report for Gov.Whitehouse.App 47.0.4, https://reports.exodus-privacy.eu.org/en/reports/722861/ (last visited Mar. 30, 2026). ↩︎
- Huawei Mobile Services, Wikipedia, https://en.wikipedia.org/w/index.php?title=Huawei_Mobile_Services&oldid=1343856094 (last visited Mar. 30, 2026). ↩︎
- 15 C.F.R. pt. 744, supp. no. 4, https://www.ecfr.gov/current/title-15/part-744. ↩︎
- Changji Esquel Textile Co. v. Raimondo, 40 F.4th 716, 720 (D.C. Cir. 2022). ↩︎
- Original designation: 84 Fed. Reg. 22,963 (May 21, 2019). Subsequent amendments: 84 Fed. Reg. 43,495; 85 Fed. Reg. 29,853; 85 Fed. Reg. 36,720; 85 Fed. Reg. 51,603; 86 Fed. Reg. 71,559; 87 Fed. Reg. 6,026; 87 Fed. Reg. 8,182; 87 Fed. Reg. 21,012; 87 Fed. Reg. 55,250. ↩︎
- Sara Salinas, Six Top US Intelligence Chiefs Caution Against Buying Huawei Phones, CNBC (Feb. 13, 2018), https://www.cnbc.com/2018/02/13/chinas-hauwei-top-us-intelligence-chiefs-caution-americans-away.html. ↩︎
- Huawei AppGallery, Wikipedia, https://en.wikipedia.org/w/index.php?title=Huawei_AppGallery&oldid=1342254869 (last visited Mar. 30, 2026) (noting AppGallery was built as a direct consequence of the Entity List designation cutting Huawei off from Google Mobile Services and the Google Play Store). ↩︎
- AppGallery Search Results for "The White House", appgallery.huawei.com (visited Mar. 30, 2026), archived at https://web.archive.org/web/20260330170305/https://appgallery.huawei.com/search/The%20White%20House. ↩︎
- 15 U.S.C. § 45(a). See, e.g., In re Facebook, Inc., FTC File No. 182-3109 (2019) (alleging misrepresentation of data collection practices and violation of prior consent order, resulting in $5 billion penalty). ↩︎
- Mickey Chandler, Mind the Gap Between Your Privacy Statement and Your Systems, Spamtacular (Feb. 14, 2025), https://www.spamtacular.com/2025/02/14/privacy-by-design-email-marketing/. ↩︎
- Cal. Civ. Code § 1798.121(a); Cal. Code Regs. tit. 11, § 7027(m)(1). ↩︎
- Wash. Rev. Code ch. 19.373. ↩︎
- Tex. Bus. & Com. Code § 541.001(29). ↩︎
- Directive 2002/58/EC, art. 5(3), as amended by Directive 2009/136/EC, recital 66. ↩︎
- Cal. Civ. Code § 1798.140(ag)(2); Regulation (EU) 2016/679, art. 28. ↩︎
- Dev Forty Five LLC, Utah Division of Corporations and Commercial Code Business Registration, Entity No. 14674165-0160, filed Mar. 18, 2026; see also Bernadette B. Tixon, Trump's White House App Earns a Community Note Days After Launch Over GPS Tracking Claims, International Business Times UK, https://www.ibtimes.co.uk/white-house-app-privacy-concerns-1789060 (last visited Mar. 30, 2026). ↩︎
- Jurassic Park (Universal Pictures 1993), at 36:08 (Dr. Ian Malcolm: "Yeah. Yeah. But your scientists were so preoccupied with whether or not they could they didn't stop to think if they should."). ↩︎
Comments
Leave a comment